Front Matter
Title: Secure User Delete
Author: Krizha Onise Cortez (armaminter)
Reviewers: Joylynne Grace Esportuno (teruterubozuuu), James Derick Billate (zcrnnn)
Created: April 2026
Status: Approved and Merged
References
Issue: [6.4] Secure User Delete - https://github.com/wyzlab/WyzQuests/issues/50
Milestone: [6] User Mgmt & Enrollment
Introduction & Goals
Problem Summary
Secure User Delete protects destructive administrator actions by requiring identity verification before permanently deleting a user account. Instead of allowing deletion immediately after clicking the delete action, the system issues a Verification Prompt that confirms the administrator's identity and generates a temporary re-authentication token.
Only verified administrators can complete deletion requests, reducing the risk of accidental or unauthorized account removal.
Goals & Non-Goals
Goals
Require administrator verification before deleting users.
Prevent unauthorized delete requests.
Issue temporary verification tokens.
Validate verification tokens before deletion.
Record deletion attempts through audit logs.
Display appropriate success and error feedback.
Non-goals
Soft-delete or account recovery.
Bulk user deletion.
Scheduled deletion.
Multi-factor authentication.
Self-service account deletion.
Glossary
Secure User Delete – Protected workflow for permanently removing user accounts.
Verification Prompt – Authentication dialog shown before destructive actions.
Re-authentication Token – Temporary token generated after successful verification.
Administrator – Authorized user permitted to delete platform users.
Audit Log – Record of successful or failed deletion attempts.
High-Level Architecture
System Diagram
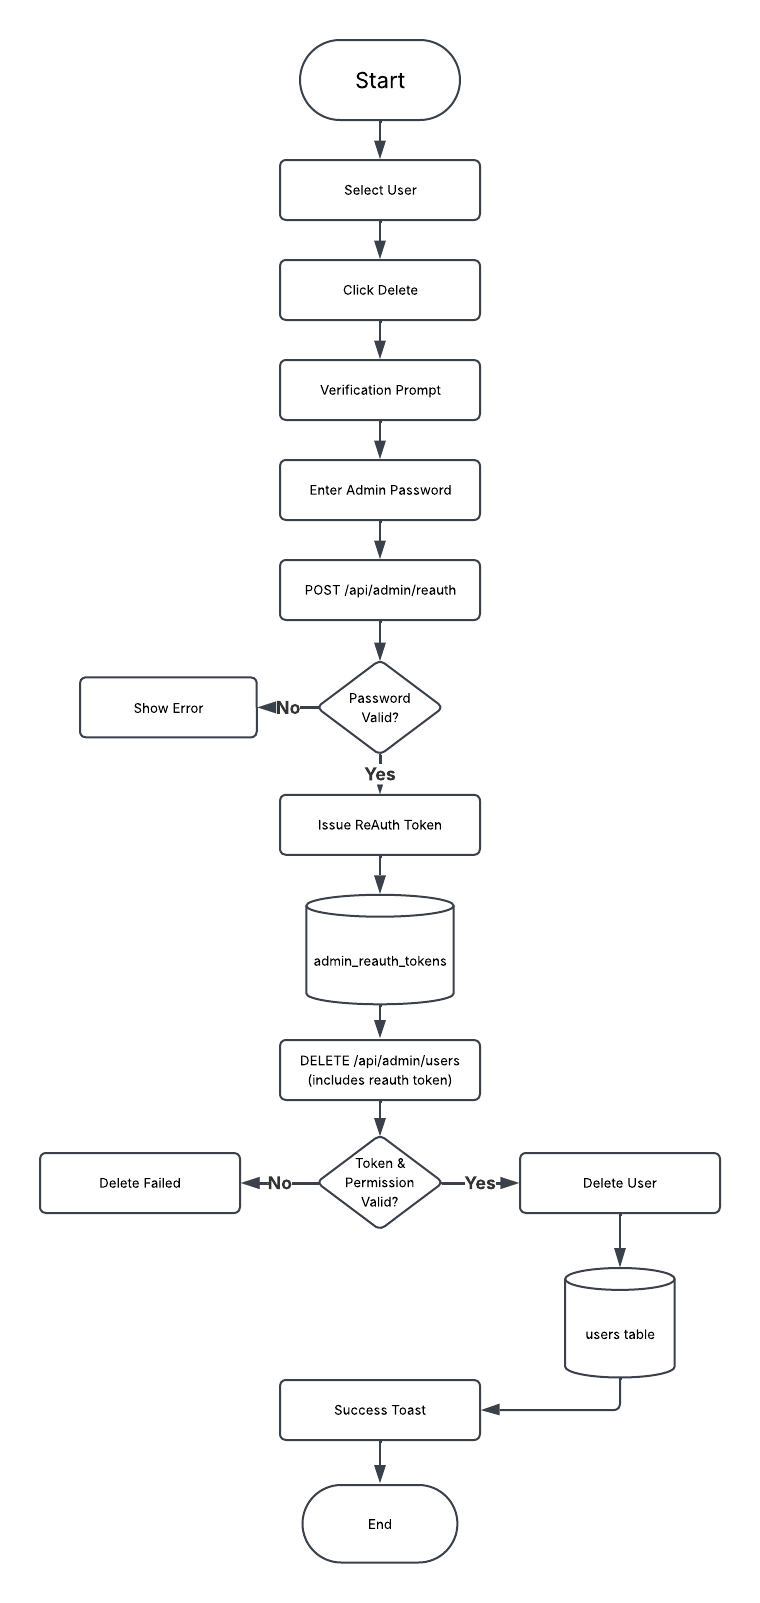
Technologies Used
Next.js App Router
React
TypeScript
Supabase
Clerk Authentication
Zod
TailwindCSS
Sonner Toast Notifications
Detailed Design & Implementation
Data Model / Schema
admin_reauth_tokens
Stores temporary verification tokens required before sensitive administrator actions.
Relevant Fields:
id
admin_clerk_id
token
expires_at
used
ip_address
created_at
Example:
{ "admin_clerk_id": "...", "token": "...", "expires_at": "...", "used": false}audit_logs
Stores security-related administrator actions.
Relevant Fields:
action
admin_id
created_at
API Specification
GET /api/admin/reauth
Returns the administrator's authentication method.
POST /api/admin/reauth
Validates administrator credentials and issues a temporary verification token.
DELETE /api/admin/users/[id]
Deletes the selected user after validating the supplied verification token.
Logic & Workflows
Administrator opens User Management.
Administrator selects Delete User.
Verification Prompt is displayed.
Administrator verifies identity.
Re-authentication token is generated.
Delete request includes the token.
Backend validates the token.
User account is deleted.
Audit log is recorded.
Success response is returned.
Infrastructure & Operations
Dependencies
Dependency | Notes |
|---|---|
Clerk Authentication | Administrator verification |
Supabase | Token storage and user data |
Zod | Request validation |
Sonner | Success/error notifications |
Monitoring & Alerting
The system validates every delete request before execution.
Validation includes:
Administrator authentication
Token validity
Token expiration
Token reuse
User existence
Current implementation relies on:
API responses
Server logs
Audit logs
Deployment Plan
Deploy re-authentication APIs.
Apply database migrations.
Verify token validation.
Verify audit logging.
Deploy User Management changes.
Verify secure deletion flow.
Testing & Quality Assurance
Test Strategy
User Deletion
Successful deletion
Unauthorized deletion
Invalid token
Expired token
Token reuse
User not found
Verification
Password verification
OAuth verification
Failed authentication
Known Limitations
Deleted users cannot be recovered.
Bulk deletion is unsupported.
MFA is not required.
Tokens expire after five minutes.
Maintenance & Support
Troubleshooting
Verification fails
Verify administrator credentials.
Verify authentication method.
Verify Clerk availability.
Delete request rejected
Verify token exists.
Verify token has not expired.
Verify token has not already been consumed.
User is not deleted
Verify user exists.
Verify administrator permissions.
Verify database operation completed successfully.
Changelog
v1.0 (July 2026)
Initial implementation of Secure User Delete.
Added Verification Prompt integration.
Added temporary re-authentication tokens.
Added audit logging support.
Document Version
1.0 – Initial internal technical guide, July 2026
